Impact and mitigations for Linux kernel vulnerability CVE-2026-98432
Users running Linux servers are advised to check security notices and apply kernel updates for vulnerability CVE-2026-98432.
Users running Linux servers are advised to check security notices and apply kernel updates for vulnerability CVE-2026-98432.
Money Forward Cloud Accounting has temporarily suspended standard PDF export due to a security response and provided alternative methods.

A permanent fix for PHP vulnerabilities has been applied to the Waiter admin screen in ver. 2.46.2.
PHP vulnerabilities have been resolved in Admin Console and Self-Service version 1.14.3.
Maintenance for critical PHP vulnerabilities was completed, restoring site display and administrative tools.
The Mackerel service infrastructure and official mackerel-agent do not use PHP and are unaffected by the disclosed PHP vulnerabilities.

Due to an XSS vulnerability in older LIFF SDK versions, LINE plans to restrict the use of affected versions in external browsers.
You must update Movable Type or apply file workarounds due to vulnerabilities that allow remote code execution and data leaks.
As a preventive measure, existing API key access and IDCF account login have been suspended for IDCF Free and IDCF Free+ plans.
All organizations can now create roles to separate report viewing permissions from operational task permissions.
LIFF v2.31.1 fixes a potential security bug in the LIFF SDK, and versions v2.20.0 through v2.31.0 have been deprecated.
You can now use 3D Secure authentication and card brand filtering in Google Pay.
After LIFF v2.31.0 was released with internal behavior changes, it was deprecated due to a security bug and faces planned usage limits.
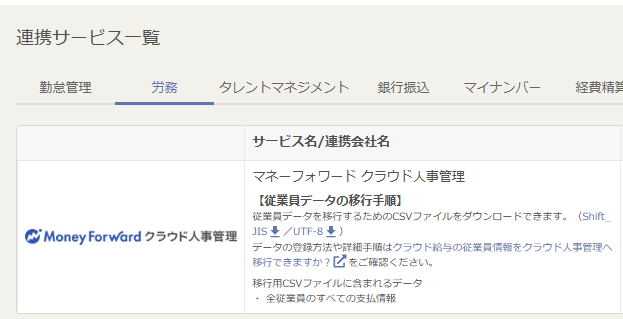
In Cloud Payroll, HR service names changed to HR Master, and users with the Payroll Admin role can now sync employee information.

Administrators can restrict Web API users and manage client ID issuance, deletion, and audit logging.
LIFF v2.30.0 added arguments to three friendship and permission methods, but was later deprecated due to a security issue with usage restrictions planned.
3D Secure authentication has migrated to Netcetera.
LIFF v2.29.2 was released with internal SDK behavior changes, then deprecated due to a security issue with usage restrictions planned.
You can now restrict the environments members can access by managing read permissions for each environment in role settings.
LIFF v2.29.1 was released with internal behavior changes, then deprecated due to a security issue with usage restrictions planned.